All Posts
7 min
min read
September 25, 2026
VISULOX: the German alternative to BeyondTrust
Privileged Access Management determines who accesses your most critical systems. Entrusting this key role to a US provider ties it to the CLOUD Act. Here is why VISULOX, as a German, on-premise alternative to BeyondTrust, restores data sovereignty in Europe.
Introduction
Data sovereignty does not begin with the storage location, but with privileged access. Privileged Access Management (PAM) is the software that decides who is allowed to access your most critical systems as an administrator or external service provider – and what is recorded in the process. Entrusting this key role to a provider subject to US law is a strategic dependency for the public sector, not merely a procurement detail.
This article explains why the market leader BeyondTrust, as a US company, is subject to the CLOUD Act, what this specifically means for government agencies and critical infrastructure operators – and how VISULOX, as a German, on-premises alternative, keeps control of privileged access within Europe.
Key Takeaways
- Privileged Access Management (PAM) is the master key system of IT: whoever controls it, controls access to all critical systems. This control belongs in European hands.
- Market leader BeyondTrust is headquartered in Johns Creek, Georgia (USA) and is owned by US private equity firms Francisco Partners and Clearlake Capital. As a result, the company is subject to US law – including the CLOUD Act.
- The US CLOUD Act obligates US providers to hand over data to US authorities, even if that data is stored in Europe. In June 2025, Microsoft confirmed to the French Senate that it could not rule out such disclosures.
- At the end of 2024, the US Treasury Department was compromised via BeyondTrust’s remote support cloud – proof that the PAM layer itself can become a gateway for attacks.
- VISULOX by amitego is an RPAM solution developed in Germany that runs on-premises and is subject exclusively to German data protection law – the sovereign alternative for government agencies and critical infrastructure.
Why PAM is the most sensitive layer of your IT
Privileged Access Management manages the most powerful accounts in the network: administrator access, service accounts, and remote maintenance by external service providers. These accounts can be used to do virtually anything—change configurations, exfiltrate data, or cover tracks. This is precisely why NIS-2 (§ 30 BSIG), ISO 27001, and the BSI minimum standards require strict control of privileged access.
The uncomfortable consequence: the PAM solution itself sees and logs your organization's most sensitive operations. Who operates this system and which jurisdiction the provider is subject to is therefore not a technical question, but a matter of sovereignty.
BeyondTrust: Market leader with a US legal framework
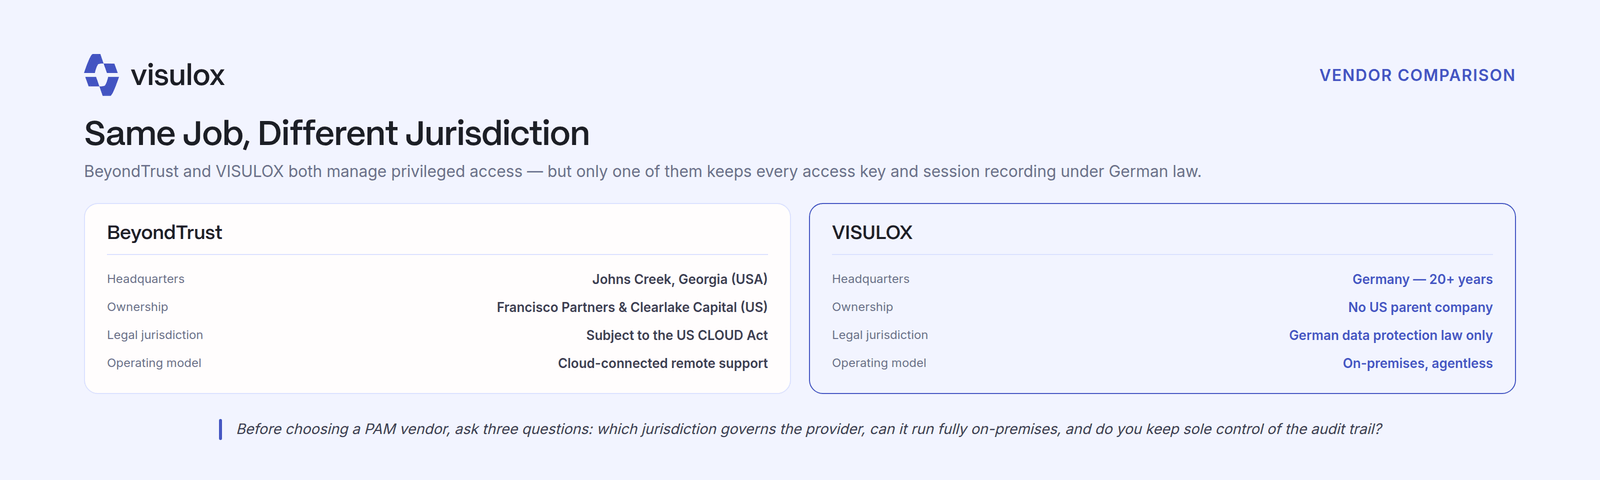
BeyondTrust is one of the established global PAM providers with a mature product portfolio—that is beyond question. However, the decisive factor for procurement in Europe is the legal framework: BeyondTrust is headquartered in Johns Creek, Georgia, and is majority-owned by the US private equity firm Francisco Partners, with a minority stake held by Clearlake Capital. It is, therefore, a US company under US ownership.
As a result, the provider is subject to US law—and that includes the CLOUD Act. This statement is not a judgment on product quality, but a fact of location and ownership structure.
The CLOUD Act: Why "servers in Europe" is not enough
The US CLOUD Act of 2018 obliges US providers to hand over data upon the order of US authorities—regardless of where in the world that data is located. A data center in Frankfurt therefore offers no protection if the provider or its parent company is subject to US law.
Microsoft admitted to the French Senate's investigative committee in June 2025 that this is not a theoretical risk: the company could not guarantee that data stored in French regions would never be transferred to US authorities without the consent of the French government. Added to this is the fundamental conflict, unresolved since the Schrems II decision (2020), between US access rights and the GDPR. The EU Data Act, applicable since September 2025, now explicitly obliges cloud providers to prevent unlawful access by third countries—an admission of how real the concern is.
For a PAM solution, this carries double the weight: we are not talking about arbitrary documents here, but the access keys and session recordings of your most critical systems.
When the protective layer becomes the gateway
The dependency is not only legal in nature. At the end of 2024, the US Treasury Department was compromised—via BeyondTrust's cloud-based remote support solution. Attackers obtained an API key for the service and exploited two zero-day vulnerabilities (CVE-2024-12356 and CVE-2024-12686) to access the agency's workstations and documents. The attack was attributed to a state-sponsored group.
The lesson here is not that "BeyondTrust is insecure"—every software has vulnerabilities. The lesson is: a central, cloud-based PAM layer from a third-country provider concentrates risk and control in a place that is beyond your reach. An on-premise architecture under your own control reduces this attack surface and keeps the keys in-house.
VISULOX: the German, sovereign alternative
This is where VISULOX by amitego comes in The remote privileged access management solution has been developed, operated, and hosted in Germany for over 20 years and is subject exclusively to German data protection law. There is no US parent company, no CLOUD Act leverage, and no non-European ownership structure.
Technically, VISULOX consolidates privileged internal and external access via a central gateway – with multi-factor authentication, just-in-time approvals, and audit-proof session recording. The solution runs on-premises and is implemented agentlessly, often in under two days. It thus meets key requirements from NIS-2 (Section 30 BSIG), ISO 27001, Article 32 GDPR, and BSI guidelines – without access data ever leaving the German legal jurisdiction.
What this means for the public sector
For government agencies, critical infrastructure operators, and public procurement, digital sovereignty is a stated goal – and increasingly a tender criterion. The question, "Which jurisdiction is the provider of our PAM solution subject to?" should therefore be at the beginning of every tender, not the end.
Three checkpoints for procurement:
- Provider's legal jurisdiction: Is the company – including its parent corporation and owners – subject exclusively to European law? Server location alone is not enough.
- Operating model: Can the solution be operated entirely on-premises and under your own control, without mandatory cloud connectivity to the manufacturer?
- Auditability: Do access logs and session recordings remain entirely in-house, ensuring they are audit-proof and under your own sovereign control?
VISULOX is designed to meet all three points. Switching to a German solution does not mean sacrificing functionality; it means regaining control over the most sensitive layer of your IT. You can calculate exactly how the transition pays off in just a few minutes using our price and license calculator on the pricing page – available as either a perpetual license or an on-prem subscription.
Contact
Your Direct Path to Secure Remote Access
Speak directly with a cybersecurity expert.
Conclusion
Privileged Access Management is the master key to your most critical systems – and therefore too sensitive to be tied to a legal framework outside of Europe. BeyondTrust is a strong market leader, but as a US company, it is subject to the CLOUD Act, and the 2024 Treasury incident shows just how real the combined risk is. VISULOX offers the sovereign alternative: developed in Germany, operated on-premises, and subject exclusively to German law. Anyone serious about data sovereignty in Europe starts with privileged access. (This article does not constitute legal advice.)
Table Of Content:
Talk to Our Experts
Speak directly with a VISULOX security expert and find out how to protect your infrastructure.
Share:
Lorem ipsum dolor sit amet, consectetur adipiscing elit. Suspendisse varius enim in eros elementum tristique. Duis cursus, mi quis viverra ornare, eros dolor interdum nulla, ut commodo diam libero vitae erat. Aenean faucibus nibh et justo cursus id rutrum lorem imperdiet. Nunc ut sem vitae risus tristique posuere.
Insights on IT Security and Privileged Access
Expert knowledge, practical tips, and the latest trends in PAM, compliance, and secure remote work — straight from the amitego team.