Remote PAM for OT & critical infrastructure
Remote maintenance for critical infrastructure – without opening your network
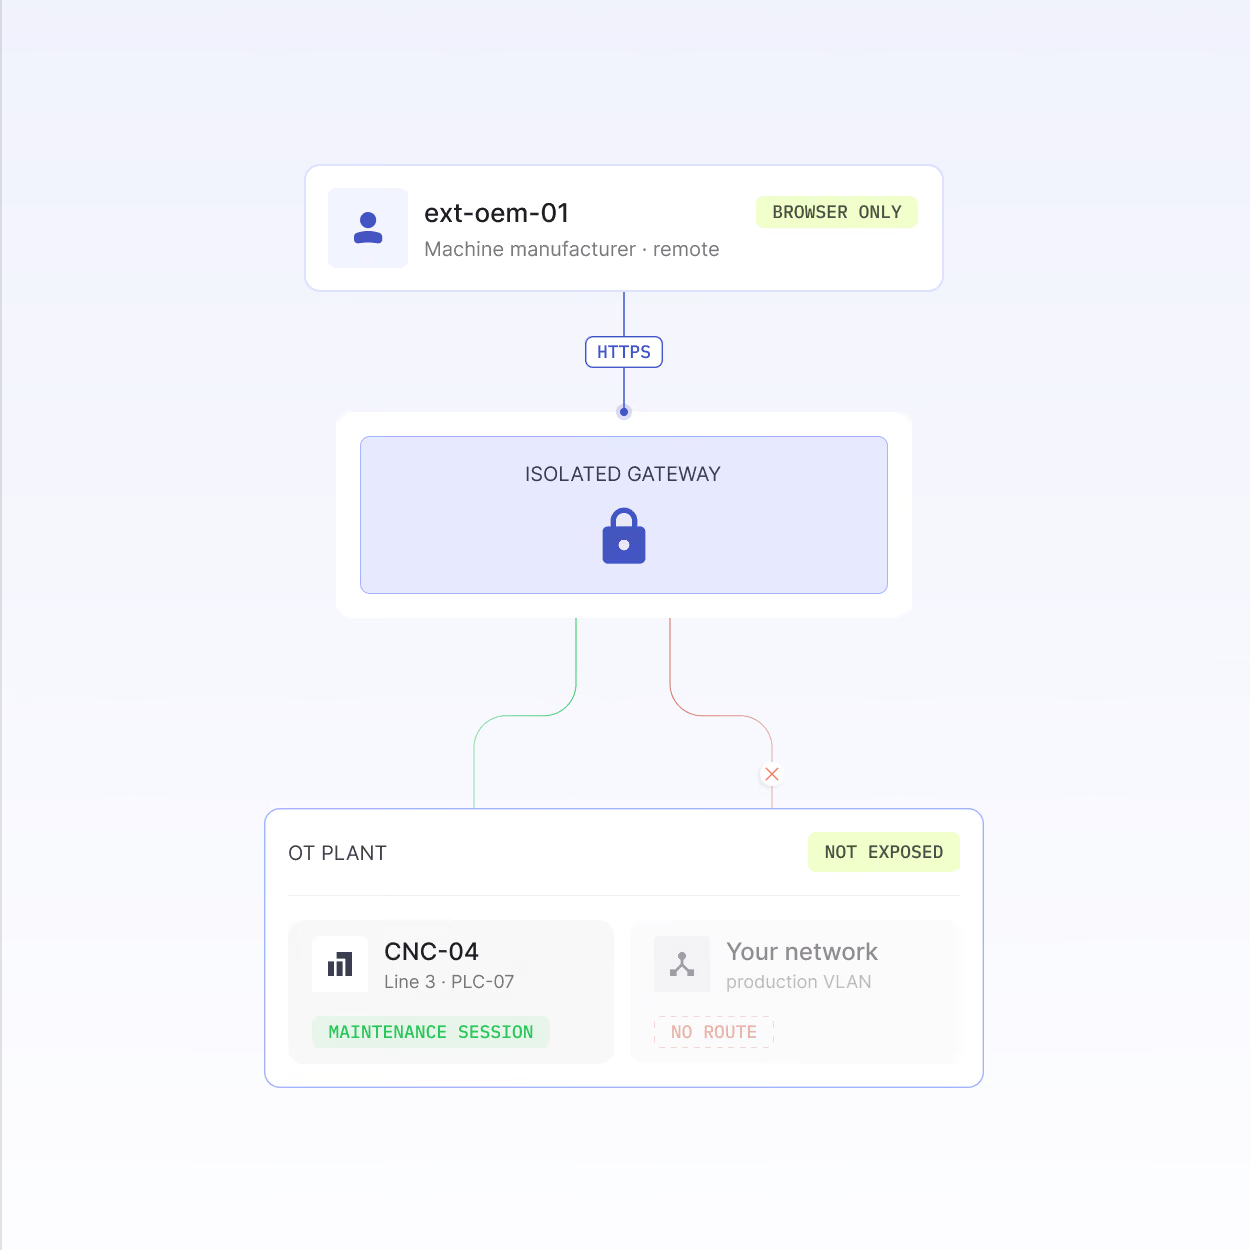
Your systems require maintenance by external vendors – but every access point is a risk to availability and security. VISULOX allows service providers to work on OT and legacy systems without ever gaining direct access to your network. Controlled, time-limited, and fully recorded.
Energy providers and industrial companies trust VISULOX

How can I allow vendors to perform maintenance without putting the facility at risk?
OT environments rely on external maintenance but are rarely built for secure remote access. Legacy protocols, permanent vendor access, and flat networks turn every maintenance task into a risk. At the same time, NIS2/BSIG require verifiable control over the entire supply chain.
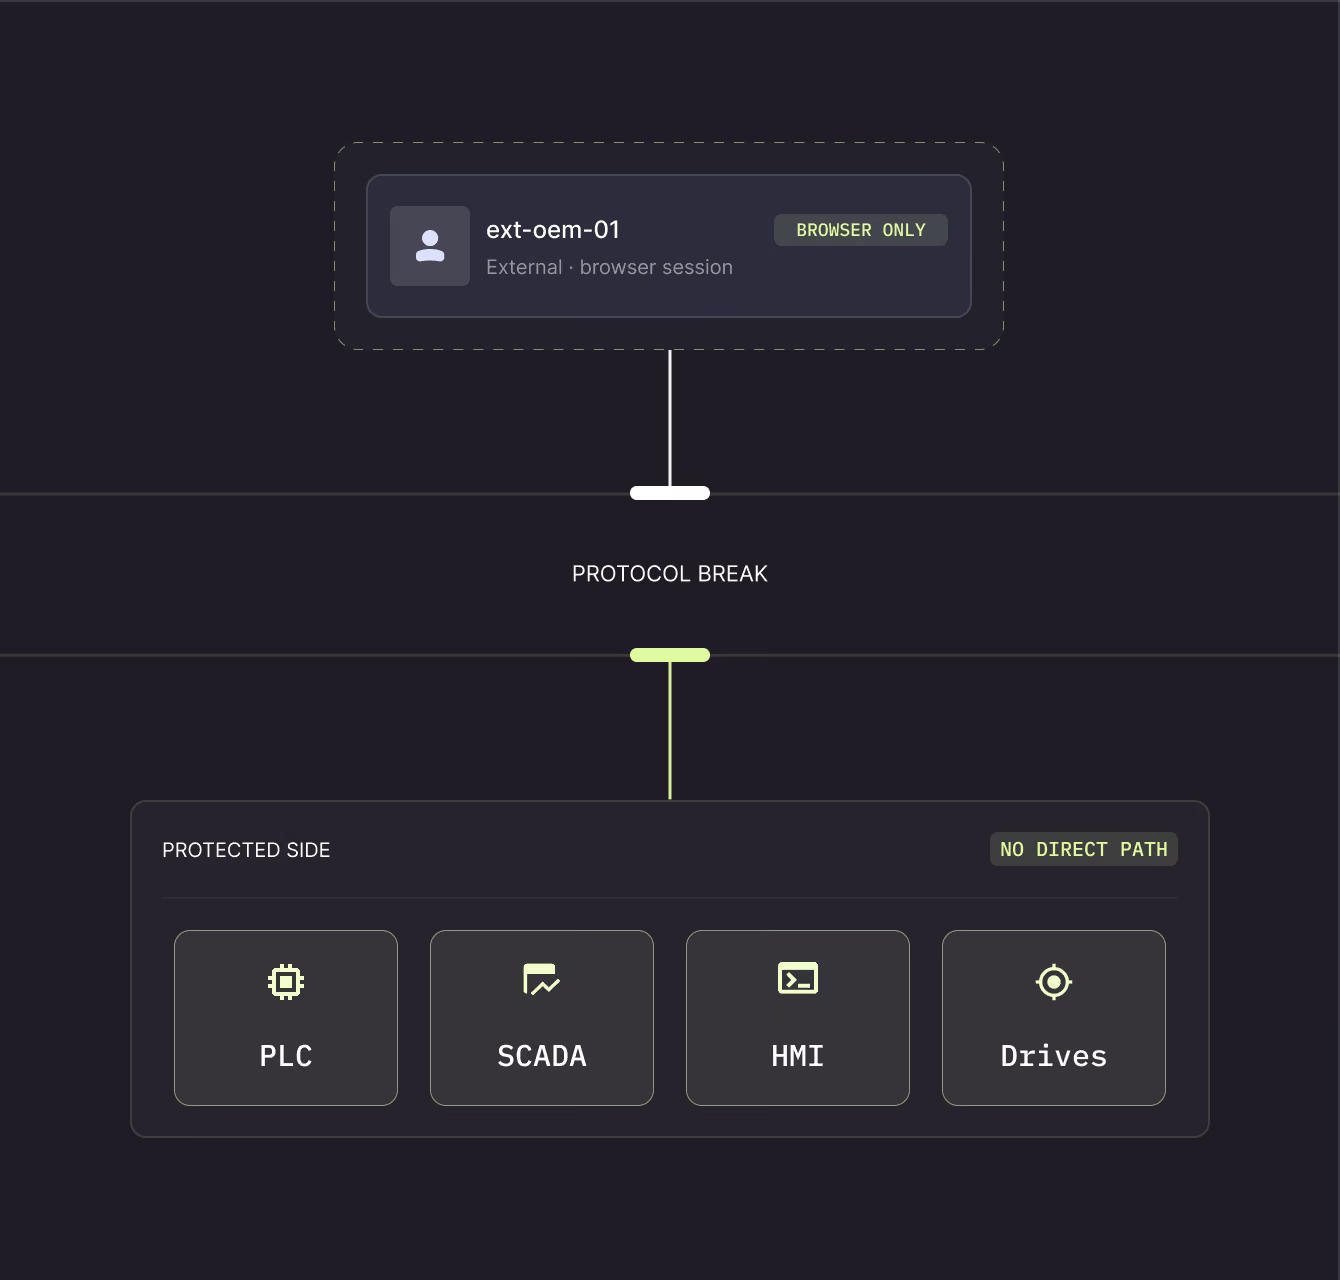
Protocol break
no direct network access to OT.
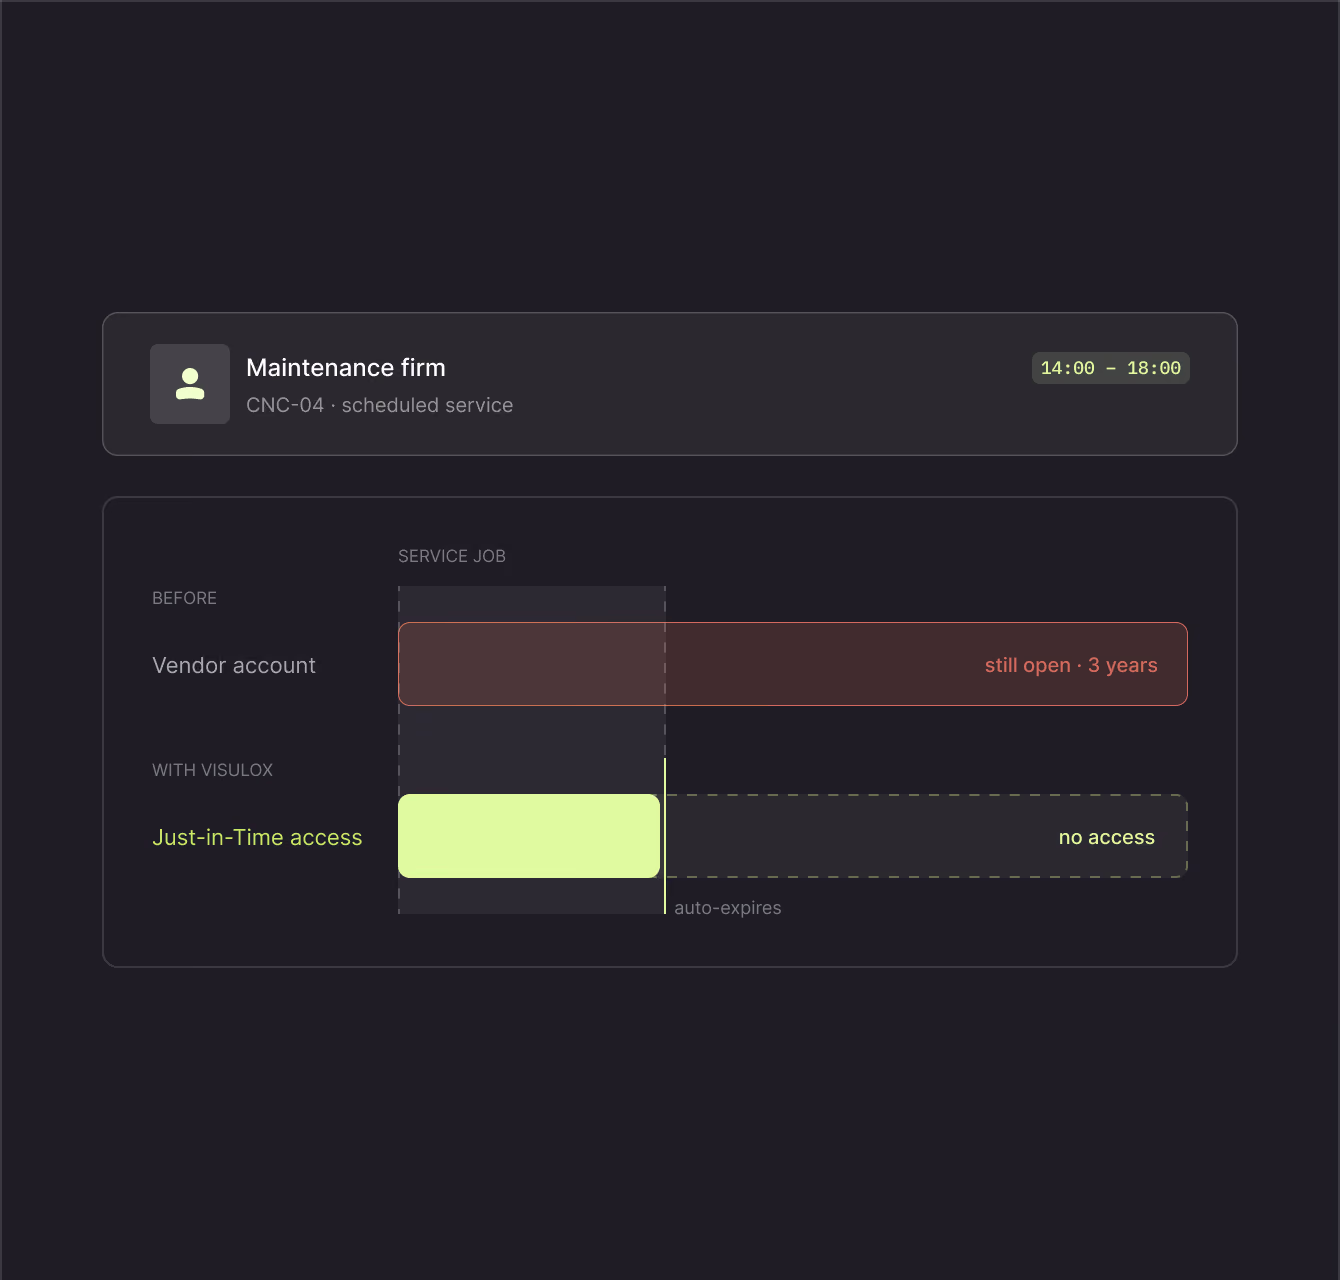
Just-in-time
Vendor access only during maintenance.
100%
recorded, auditable sessions.
Isolation
Maintenance without a direct line into your facility
External users work via a browser in a segregated zone. Protocol breaking ensures there is never a direct connection to the OT infrastructure.
External Access: Granular, agentless, and without coordination chaos
Internal Access Management: Secure and simplify work from anywhere
Built for Zero Trust: Easily implement all building blocks such as Multi-Factor Authentication and Just-in-Time access
Always traceable: Automated compliance reporting, tamper-proof recordings, and audit trails
Gateway architecture without direct network access
Connections via RDP, SSH, VNC, HTTPS
Securing IT and OT systems together
No VPN, no flat networks
Just-in-time
No permanent access for external technicians
Access is created for a limited time and a specific purpose. No standing privileges for maintenance companies, no forgotten access.
External Access: Granular, agentless, and without coordination chaos
Internal Access Management: Secure and simplify work from anywhere
Built for Zero Trust: Easily implement all building blocks such as Multi-Factor Authentication and Just-in-Time access
Always traceable: Automated compliance reporting, tamper-proof recordings, and audit trails
Just-in-time access, zero standing privileges
Grant and revoke access with a click
Multi-factor authentication
Break-glass for emergencies
Control
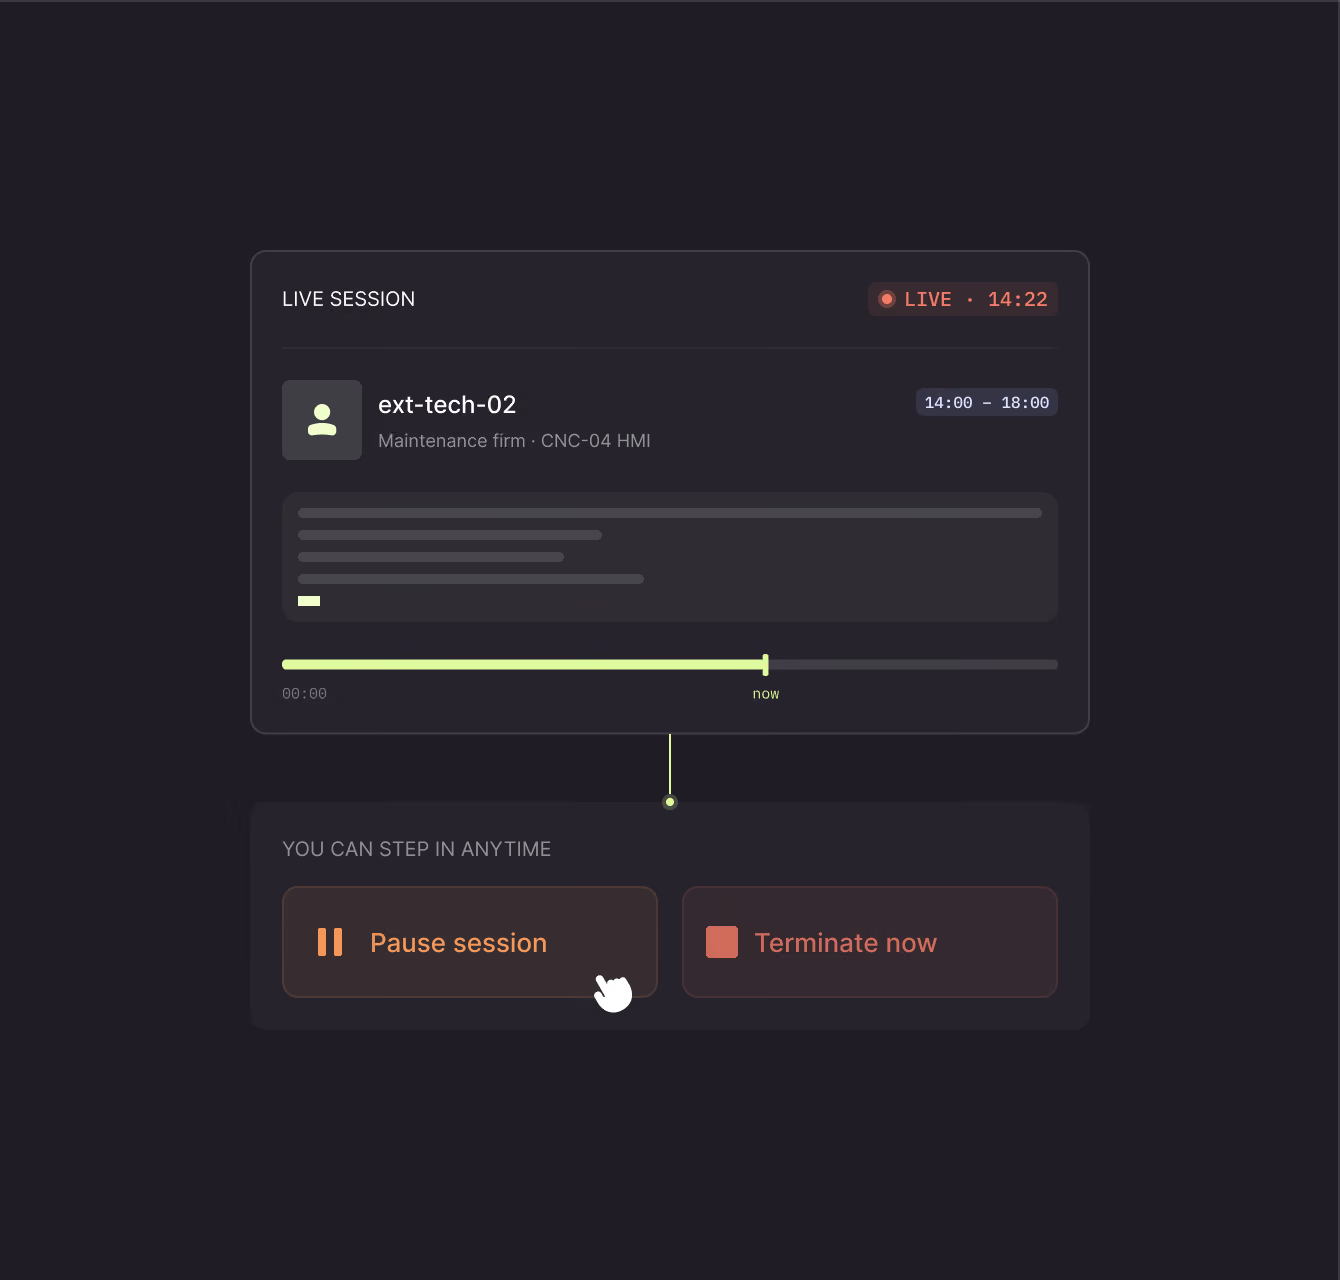
Never leave external personnel unattended near critical systems
You can see who is working on what in real time and intervene at any moment. Every session is recorded for audit purposes.
External Access: Granular, agentless, and without coordination chaos
Internal Access Management: Secure and simplify work from anywhere
Built for Zero Trust: Easily implement all building blocks such as Multi-Factor Authentication and Just-in-Time access
Always traceable: Automated compliance reporting, tamper-proof recordings, and audit trails
Live visibility and intervention capabilities
Four-eyes principle for critical maintenance
Audit-proof session recordings
Cross-server monitoring
Reliability
Built for critical infrastructure, reliable for the long term
Developed in Germany/Switzerland, independent of geopolitical risks. Custom development also available for legacy systems.
External Access: Granular, agentless, and without coordination chaos
Internal Access Management: Secure and simplify work from anywhere
Built for Zero Trust: Easily implement all building blocks such as Multi-Factor Authentication and Just-in-Time access
Always traceable: Automated compliance reporting, tamper-proof recordings, and audit trails
German/Swiss development, no third-party dependencies
Customization for legacy systems
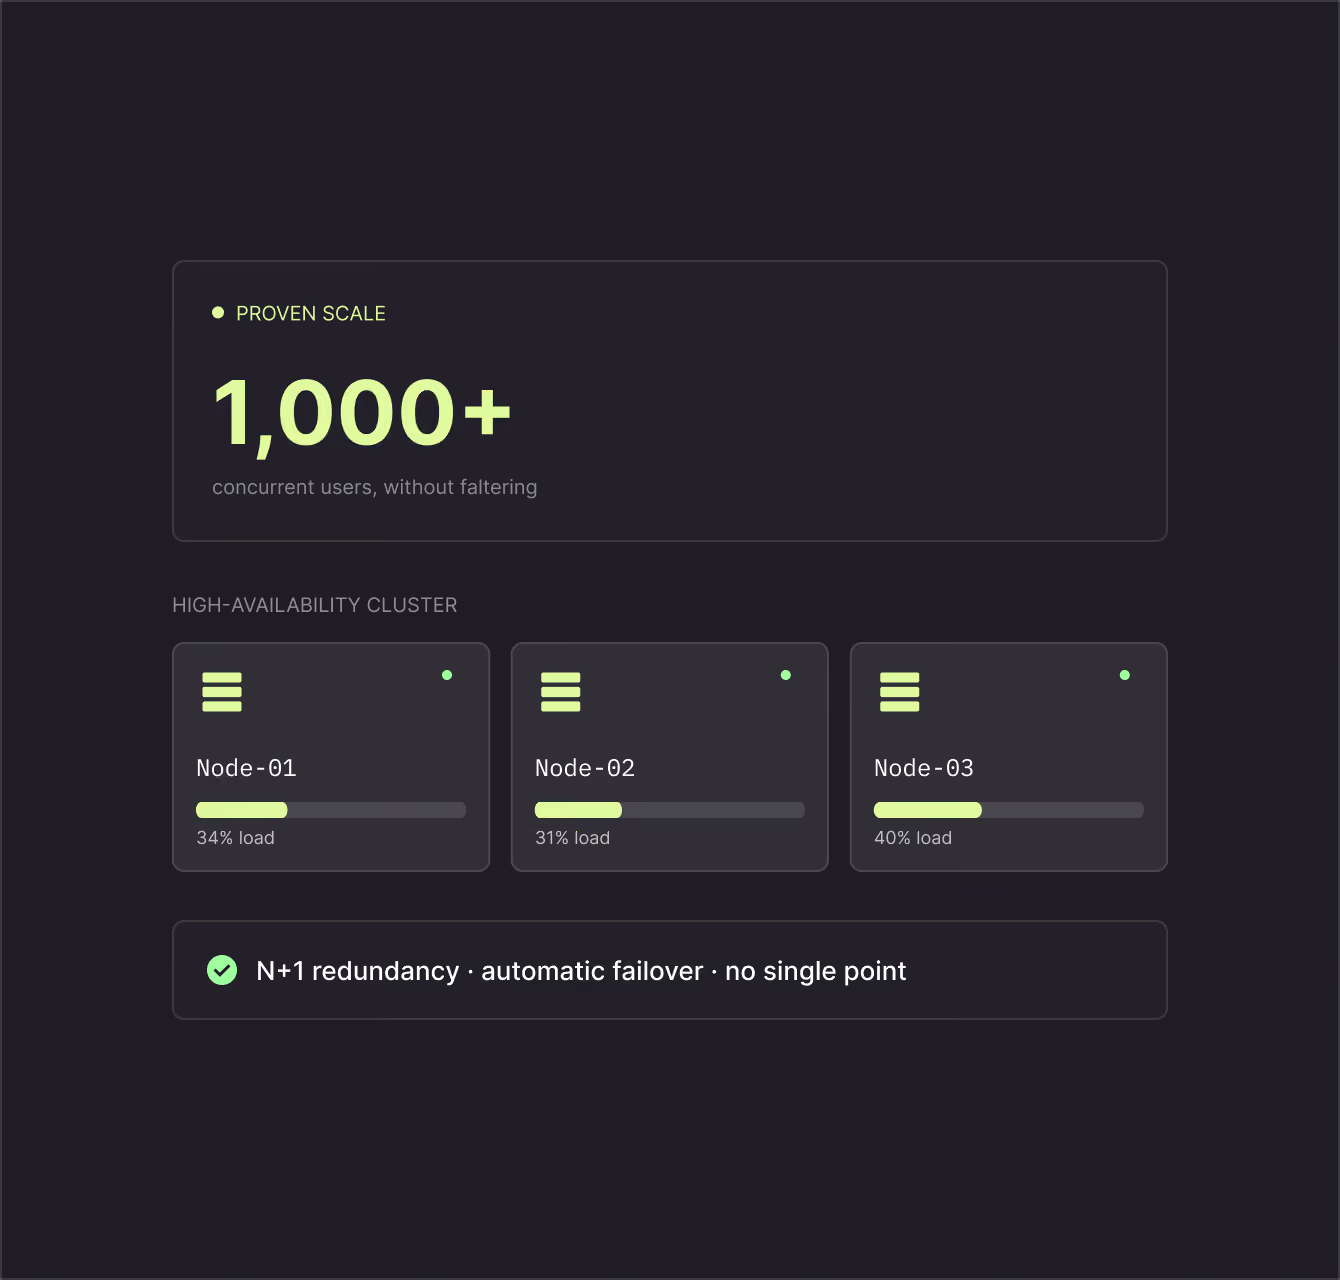
High-availability cluster, 1,000+ concurrent users
NIS2/BSIG-compliant, ISO 27001
Kundenstimmen
Why over 450 IT teams secure their systems with VISULOX
We use VISULOX as a gateway to secure our customer support environment. Through VISULOX, we establish a secure connection with our customers to assist them in implementing our products. VISULOX provides a secure method with key and video recording that meets the highest security and audit standards. Support is quick and personal.
VISULOX enables the management of information security through the privileged access control of users to various infrastructures with centralized management.
VISULOX works flawlessly, and the IT support is exceptionally reachable in emergencies. Moreover, the team also assists with other concerns, even if they are not directly related to VISULOX.
We can be sure that our R&D data is accessed exclusively by us. VISULOX gives us the assurance that external service providers are never 'unattended' and that no one can access critical information or, in the worst case, even share it.
Secure access to IT infrastructures can be presented very transparently. The system operates stably, even with over 1000 users. Our implementation of ISO 27001 is significantly supported, especially for large infrastructures.

VISULOX monitors service provider activities across servers – privileged multiple accounts are eliminated. Together with amitego, we have developed a transparent, auditable control system that precisely documents who did what and when.
Highly powerful, mature, and secure for privileged remote access by external service providers. First-class support and a forward-thinking development team at amitego. We are in close, ongoing contact with the vendor and can actively contribute to the product's evolution. Customer requests are addressed promptly.
Will operations remain safe and stable?

No network access
Protocol break keeps external parties physically out of the OT.
No permanent access
Just-in-time access instead of forgotten vendor accounts.
No availability risk
Agentless, no interference with system controls.
No external dependencies
Sovereign solution from Germany/Switzerland.
FAQ
Antworten auf die häufigsten Fragen aus dem Finanzsektor.
What is Remote Privileged Access Management (Remote PAM) with VISULOX?
Remote Privileged Access Management (Remote PAM) controls and protects privileged access to IT systems from remote locations — by administrators, external service providers, or partners. VISULOX implements this approach consistently: access is managed centrally, granted on a time-limited basis, uniquely assigned to an individual, and fully documented. Direct connections to the target infrastructure are technically prevented. This ensures control, traceability, and security at all times.
How does VISULOX differ from classic VPN or PAM solutions?
Conventional VPN solutions grant broad network access without fine-grained control. Classic PAM solutions are often complex, costly, and designed primarily for internal users. VISULOX combines the advantages of both approaches: a gateway architecture without direct network access, time-limited just-in-time access, complete session recording, and an agentless architecture. The result: maximum control with minimal administrative effort — purpose-built for secure external access.
How does VISULOX support a Zero Trust strategy?
VISULOX implements Zero Trust consistently: no user has standing access rights — permissions are granted only when needed, based on the least-privilege principle (just-in-time access). Direct network connections are technically prevented through a protocol break. Every session is fully recorded and uniquely assigned to a single individual. This creates a zero-standing-privileges model that also securely integrates external service providers and partners.
Why does VISULOX have a lower total cost of ownership (TCO)?
VISULOX is ready to use within a few days — without complex implementation projects and without changes to endpoints. Its agentless architecture significantly reduces maintenance effort. Licensing by concurrent users avoids hidden costs. Together with integrated German-language support and the avoidance of costs from security incidents, VISULOX demonstrably reduces complexity and operating costs.
Is VISULOX suitable for enterprise environments?
Remote Privileged Access Management (Remote PAM) governs and secures privileged access to IT systems from remote locations — by administrators, external service providers, or partners. VISULOX implements this approach consistently: access is granted centrally, time-limited, uniquely assigned to an individual, and fully documented. Direct connections to the target infrastructure are technically prevented, ensuring control, traceability, and security at all times.